Smart contracts have changed the way blockchain applications handle transactions, digital assets, and automated agreements. Instead of depending entirely on a centralized server or intermediary, smart contracts can execute predefined rules on a blockchain. Solidity has become one of the leading programming languages for building these contracts, particularly across Ethereum and other EVM-compatible networks.
However, the growing use of smart contracts has also increased the importance of security. A traditional software application can often be patched when a vulnerability is discovered. Smart contracts can be considerably more difficult to correct after deployment, especially when they control valuable assets or interact with other blockchain protocols. A small coding mistake can therefore create consequences that extend beyond a single application.
For Solidity developers, security needs to be considered throughout the development lifecycle rather than added as a final step. Careful architecture, testing, access control, code review, and monitoring can all contribute to safer smart-contract development.
Why Smart Contract Security Matters
Smart contracts operate in an environment where transactions are publicly recorded and contract logic can be executed by users or other contracts. Depending on the application’s design, a contract may hold tokens, process payments, manage voting systems, or control access to digital resources.
This creates a unique security challenge. Developers are not only protecting application data; they may also be protecting assets and enforcing financial or governance rules. If contract logic allows an unauthorized action, the blockchain network may execute that action according to the code.
Security therefore begins with understanding what the contract is supposed to do and identifying what users should and should not be able to do.
Start With a Secure Contract Design
Security problems can originate before the first line of Solidity code is written. Developers should clearly define contract responsibilities, user permissions, expected state changes, and interactions with external contracts.
A simple architecture can often be easier to test and review than unnecessarily complicated code. Developers should avoid adding features that are not required for the application’s purpose because every additional function can introduce another potential source of bugs.
The contract’s assumptions should also be documented. For example, if a function expects a particular caller or external service to behave honestly, that assumption should be visible during development and security review.
Use Strong Access Control
Access control is one of the most important security areas in smart-contract development. Contracts frequently contain administrative functions that can change settings, pause operations, mint tokens, upgrade implementations, or withdraw funds.
If these functions are not properly restricted, unauthorized users may be able to perform actions intended only for administrators or specific roles.
Developers should clearly separate ordinary user functionality from privileged operations. Role-based access-control approaches can be useful when a contract has multiple categories of authorized users.
Common areas that require access-control review include:
- Administrative functions
- Token minting and burning
- Contract upgrades
- Emergency controls
- Treasury or asset management
Access permissions should be tested independently rather than assuming that a modifier or authorization check works correctly simply because the code compiles.
Follow the Checks-Effects-Interactions Pattern
External contract calls are another major area of concern. A smart contract may interact with tokens, decentralized exchanges, lending protocols, or other external contracts. These calls can introduce unexpected behavior.
One widely used development principle is the checks-effects-interactions pattern. The basic idea is to validate conditions first, update the contract’s internal state, and then interact with an external contract where appropriate.
This approach can help reduce certain reentrancy risks. Reentrancy occurs when an external call allows another execution path to enter a contract before the original operation has completed.
Developers should not treat a single coding pattern as a complete security solution, but following established design practices can reduce common vulnerabilities.
Protect Against Reentrancy
Reentrancy has historically been one of the most discussed smart-contract vulnerabilities. It can occur when a contract makes an external call and the receiving contract uses that opportunity to call back into the original contract before its state has been updated appropriately.
Modern Solidity development includes several approaches for reducing this risk. Developers may structure state changes before external calls, use reentrancy protection mechanisms where appropriate, and minimize unnecessary external interactions.
The important point is that developers should understand why a particular protection is being used. Simply adding a security modifier without understanding the contract’s execution flow may leave other vulnerabilities unresolved.
Validate Inputs and State Changes
Smart contracts should never assume that users will provide valid or expected inputs. Public functions can receive a wide range of values, and malicious users may deliberately attempt to trigger unusual behavior.
Input validation should therefore be part of contract design. Developers need to check conditions such as valid addresses, acceptable amounts, sufficient balances, correct states, and authorized callers.
State transitions deserve similar attention. A contract should only move from one state to another when the required conditions are satisfied. Unexpected state changes can create inconsistencies that become difficult to correct after deployment.
Be Careful With External Contracts
Interacting with another smart contract introduces dependencies that developers do not completely control. The external contract may have unexpected behavior, change over time, or contain its own vulnerabilities.
Developers should understand the contracts they interact with and avoid making unnecessary assumptions about their behavior. Token standards can also have implementation differences, meaning that developers should test integrations rather than relying only on theoretical compatibility.
External calls should be treated as security-sensitive operations, especially when they can influence balances or contract state.
Handle Arithmetic Carefully
Financial applications often involve calculations, balances, percentages, exchange rates, and other numerical operations. Incorrect arithmetic can produce serious application-level problems.
Modern versions of Solidity include built-in checks for arithmetic overflow and underflow in standard operations, reducing some historical risks. However, developers still need to check calculations for logical errors.
A calculation can be mathematically valid but still produce the wrong business result because of incorrect units, rounding, precision assumptions, or an inappropriate formula.
For financial contracts, developers should test calculations with normal values, boundary conditions, very large values, and values that produce rounding effects.
Keep Gas Efficiency and Security Balanced
Gas optimization is useful because inefficient smart contracts can make transactions more expensive. However, optimization should not weaken security or make the code unnecessarily difficult to understand.
Developers should first make the contract correct and secure, then identify meaningful opportunities to reduce unnecessary computation or storage operations.
Overly complicated optimization can sometimes make security reviews more difficult. Readable code can be a security advantage because reviewers can more easily understand how the contract behaves.
Use Automated Testing and Security Tools
Automated tools can help Solidity developers identify problems before deployment. Static analysis tools can examine contract code for suspicious patterns, while automated test frameworks can execute large numbers of test cases.
Testing should cover both normal functionality and failure scenarios. Developers should deliberately test what happens when users provide invalid inputs, call functions without authorization, repeat operations, or interact with the contract in unexpected sequences.
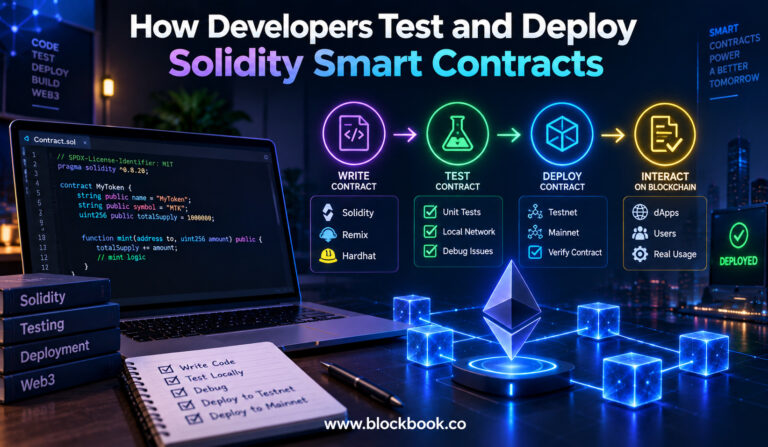
A useful security workflow may include:
- Unit and integration testing.
- Static analysis and automated vulnerability checks.
- Fuzz testing with unexpected inputs.
- Manual code review and security analysis.
Automated tools are valuable, but they should not be treated as proof that a contract is secure. They may identify known patterns while missing application-specific logic problems.
Use Fuzzing and Invariant Testing
Fuzz testing has become an increasingly useful technique for smart-contract development. Instead of relying only on manually selected inputs, fuzzing tools generate many different values and transaction scenarios to search for unexpected behavior.
Invariant testing takes the approach further by defining conditions that should always remain true. For example, a token contract may have rules governing total supply or account balances. Developers can test whether those conditions continue to hold after many different sequences of transactions.
These approaches are especially useful for complex protocols where manually predicting every possible interaction is difficult.
Review Upgradeable Contracts Carefully
Upgradeable smart contracts can allow developers to modify contract logic after deployment. This can be useful for fixing bugs or introducing improvements, but upgradeability introduces additional security considerations.
The upgrade mechanism itself must be protected. Developers need to determine who can authorize an upgrade, how implementation addresses are managed, and what happens if administrative privileges are compromised.
A contract should not use an upgrade system simply because it is convenient. The architecture should match the application’s requirements and threat model.
Use Audits as Part of a Larger Security Process
Security audits can provide valuable independent review before a major contract is deployed. Professional auditors can examine contract architecture, implementation details, access controls, economic logic, and known vulnerability patterns.
An audit should not be viewed as a guarantee that a contract contains no vulnerabilities. Smart-contract security is an ongoing process, and changes made after an audit may introduce new issues.
Developers should address identified findings, document changes, and ensure that the audited code matches the code ultimately deployed.
Monitor Contracts After Deployment
Security work continues after a smart contract reaches a blockchain network. Developers can monitor transactions, events, contract balances, administrative actions, and unusual activity.
Monitoring systems can help teams detect suspicious behavior and respond according to predefined procedures. Emergency mechanisms such as pause functionality can sometimes provide an additional layer of protection, although they also require secure access controls and careful design.
Post-deployment monitoring is especially important for contracts that handle significant transaction volumes or interact with multiple protocols.
Solidity Security Practices at a Glance
| Security Practice | Main Purpose | Development Benefit |
| Access control | Restrict privileged actions | Prevent unauthorized operations |
| Input validation | Reject unsafe or invalid values | Improve contract reliability |
| Reentrancy protection | Reduce external-call risks | Strengthen transaction safety |
| Automated testing | Check expected behavior | Detect bugs early |
| Fuzz and invariant testing | Explore unexpected states | Find complex logic problems |
| Code review | Examine implementation and design | Improve security confidence |
| Auditing | Independent security assessment | Identify additional risks |
| Monitoring | Observe deployed behavior | Detect unusual activity |
Building a Security-First Development Culture
One of the biggest changes in blockchain development is the need to consider security from the beginning. Security should influence architecture, coding practices, testing, deployment, and monitoring rather than being handled only immediately before launch.
Development teams can improve this process by maintaining clear documentation, conducting peer reviews, using automated testing in development pipelines, and carefully controlling deployment permissions.
The goal is not simply to eliminate every possible bug. No software development process can guarantee that. Instead, the objective is to systematically identify and reduce technical and operational risks before and after deployment.
Conclusion
Smart-contract security is a fundamental part of Solidity development. Because contracts can control digital assets and execute according to predefined blockchain rules, developers need to take a more cautious approach than simply writing code that produces the expected result under normal conditions.
Strong access control, careful external interactions, reentrancy protection, input validation, arithmetic testing, automated analysis, fuzzing, audits, and post-deployment monitoring can all contribute to a stronger security process.
As decentralized applications continue to evolve, Solidity developers will increasingly need to combine programming skills with security engineering practices. A security-first development lifecycle can help teams identify vulnerabilities earlier, reduce avoidable risks, and build blockchain applications that are easier to review, maintain, and operate.
FAQs
Why is security especially important for Solidity smart contracts?
Smart contracts can manage digital assets and execute transactions automatically. Depending on their design, vulnerabilities can therefore affect both application behavior and user funds.
What is reentrancy in Solidity?
Reentrancy occurs when an external interaction allows execution to return to a contract before the original operation has completed. Developers use careful state-management patterns and other protections to reduce related risks.
Is Solidity automatically secure?
No. Solidity provides language features and safety mechanisms, but the security of a smart contract ultimately depends on its architecture, implementation, testing, and operational controls.
Are smart-contract audits enough to guarantee security?
No. An audit can identify vulnerabilities and design concerns, but it does not guarantee that a contract is completely free from bugs. Changes after an audit can also introduce new risks.
What is fuzz testing in smart-contract development?
Fuzz testing automatically supplies a large variety of inputs and transaction scenarios to search for unexpected contract behavior that may not be discovered through ordinary test cases.
About the Author